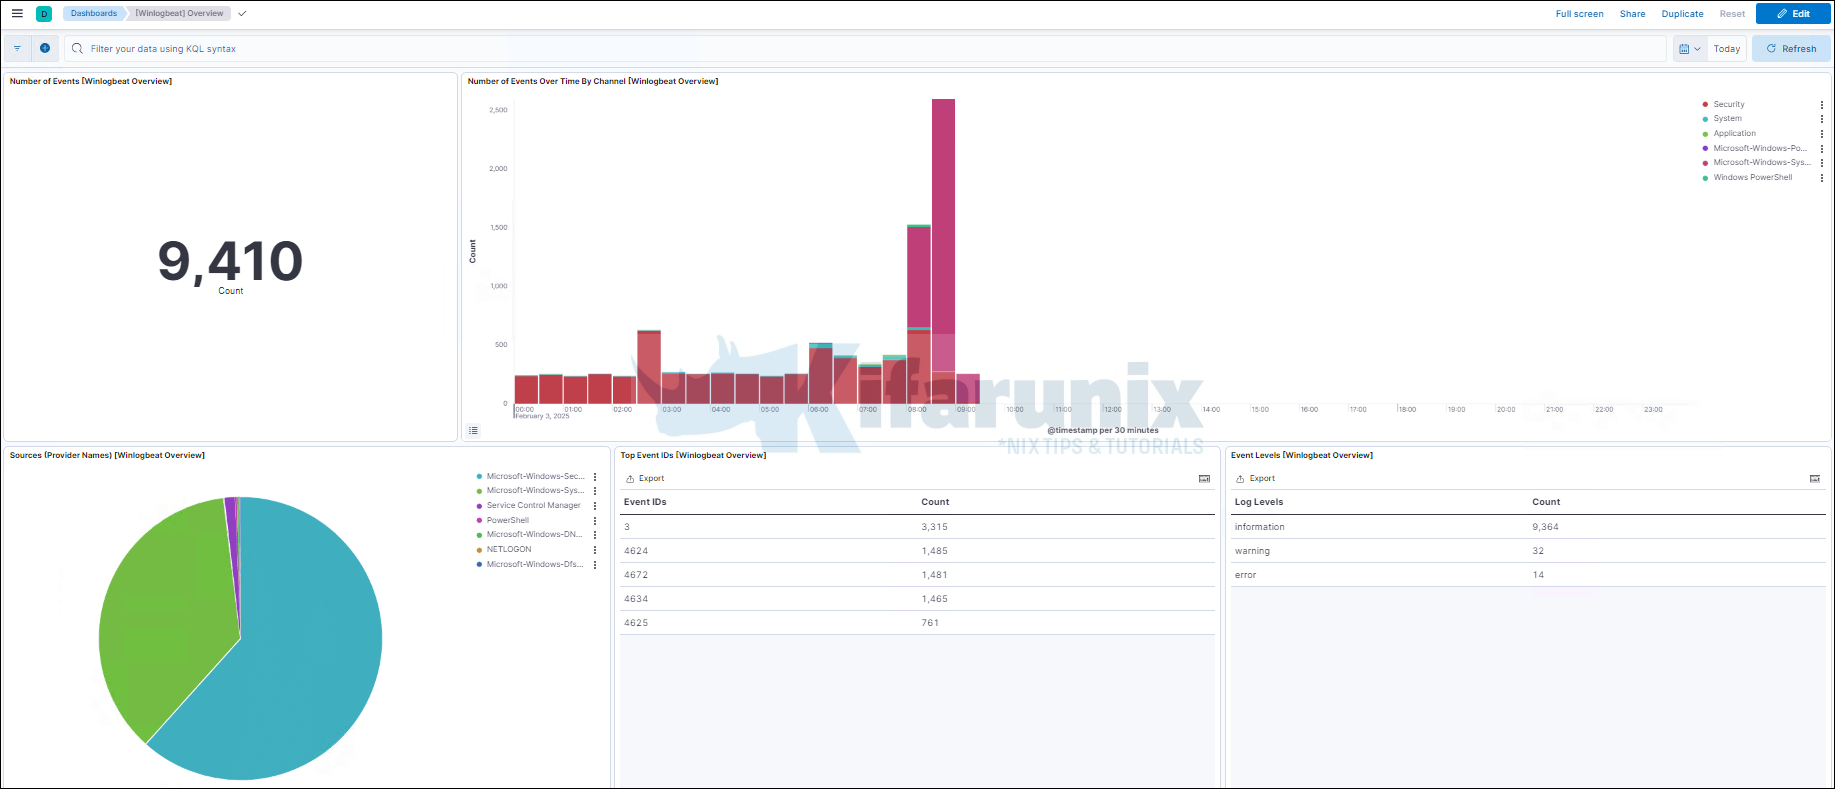
Send Windows logs to Elastic Stack using Winlogbeat and Sysmon
In this guide, we are going to learn how to send Windows logs to Elastic Stack using Winlogbeat and Sysmon. Winlogbeat is an Elastic Beat
In this guide, we are going to learn how to send Windows logs to Elastic Stack using Winlogbeat and Sysmon. Winlogbeat is an Elastic Beat
In this guide, we are going to learn how to install Elastic Stack 7 on Fedora 30/Fedora 29/CentOS 7. Elastic Stack comprises of: Elasticsearch is
Welcome to our guide on how to debug Logstash Grok filters. Grok filter uses regular expressions to parse unstructured event data into fields. It is

In this tutorial, you will learn how to install Cortex on Ubuntu 22.04/Ubuntu 20.04. Cortex is a powerful observable analysis and active response engine that
In this tutorial, you will learn how to install Fleet osquery manager on Rocky Linux. According to its Github repository, “Fleet is the most widely
In this tutorial, you will learn how to install Wazuh agents on Ubuntu/Debian systems. Wazuh operates in server-client architecture. It is made up of a
This guide will take you through how to install Elasticsearch 7.x on CentOS 7/Fedora 29. Elasticsearch is the heart of Elastic Stack. Our previous guide
Welcome to our tutorial on how to monitor squid access logs with Graylog server. Graylog is a leading open-source log management tool that provides real time
In this tutorial, you will learn how to install latest Grafana on Debian 10. Grafana is an open source analytics and monitoring solution that enables you
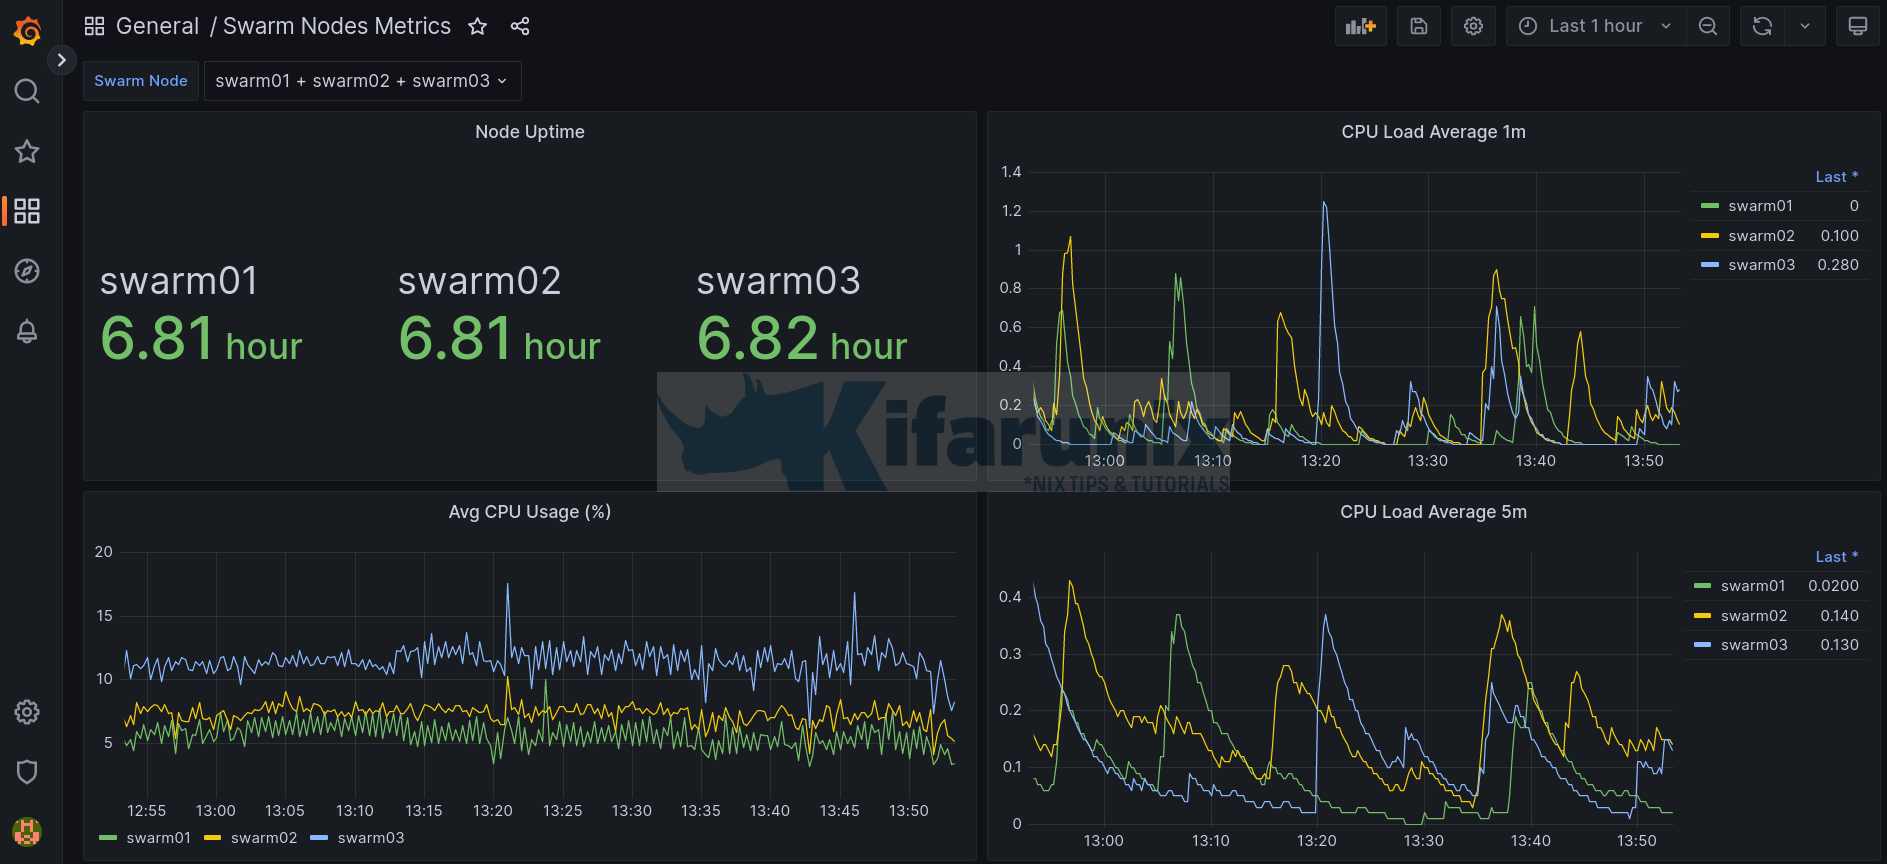
How can I monitor Docker swarm node metrics? In this tutorial, you will learn how to monitor Docker swarm node metrics using Grafana. Prometheus node