Create Squid Logs Extractors on Graylog Server
In this guide, we are going to go over how to create squid logs extractors on Graylog server. If you have pushed your Squid access
In this guide, we are going to go over how to create squid logs extractors on Graylog server. If you have pushed your Squid access
Welcome to our tutorial on how to monitor squid access logs with Graylog server. Graylog is a leading open-source log management tool that provides real time
This is a simple tutorial on how to search and delete specific records from Elasticsearch index. Elasticsearch ships with a delete_by_query API that enables you
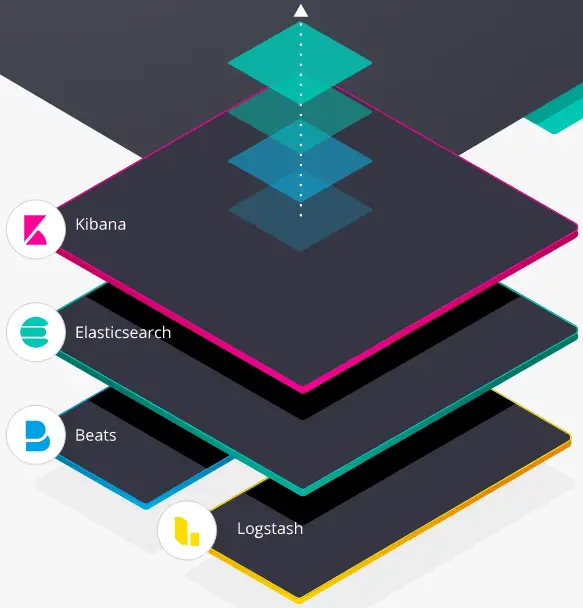
Today we are going to learn how to install Elasticsearch 7.x on Ubuntu 18.04/Debian 9.8. Elasticsearch is an open source, distributed, RESTful, JSON-based search and
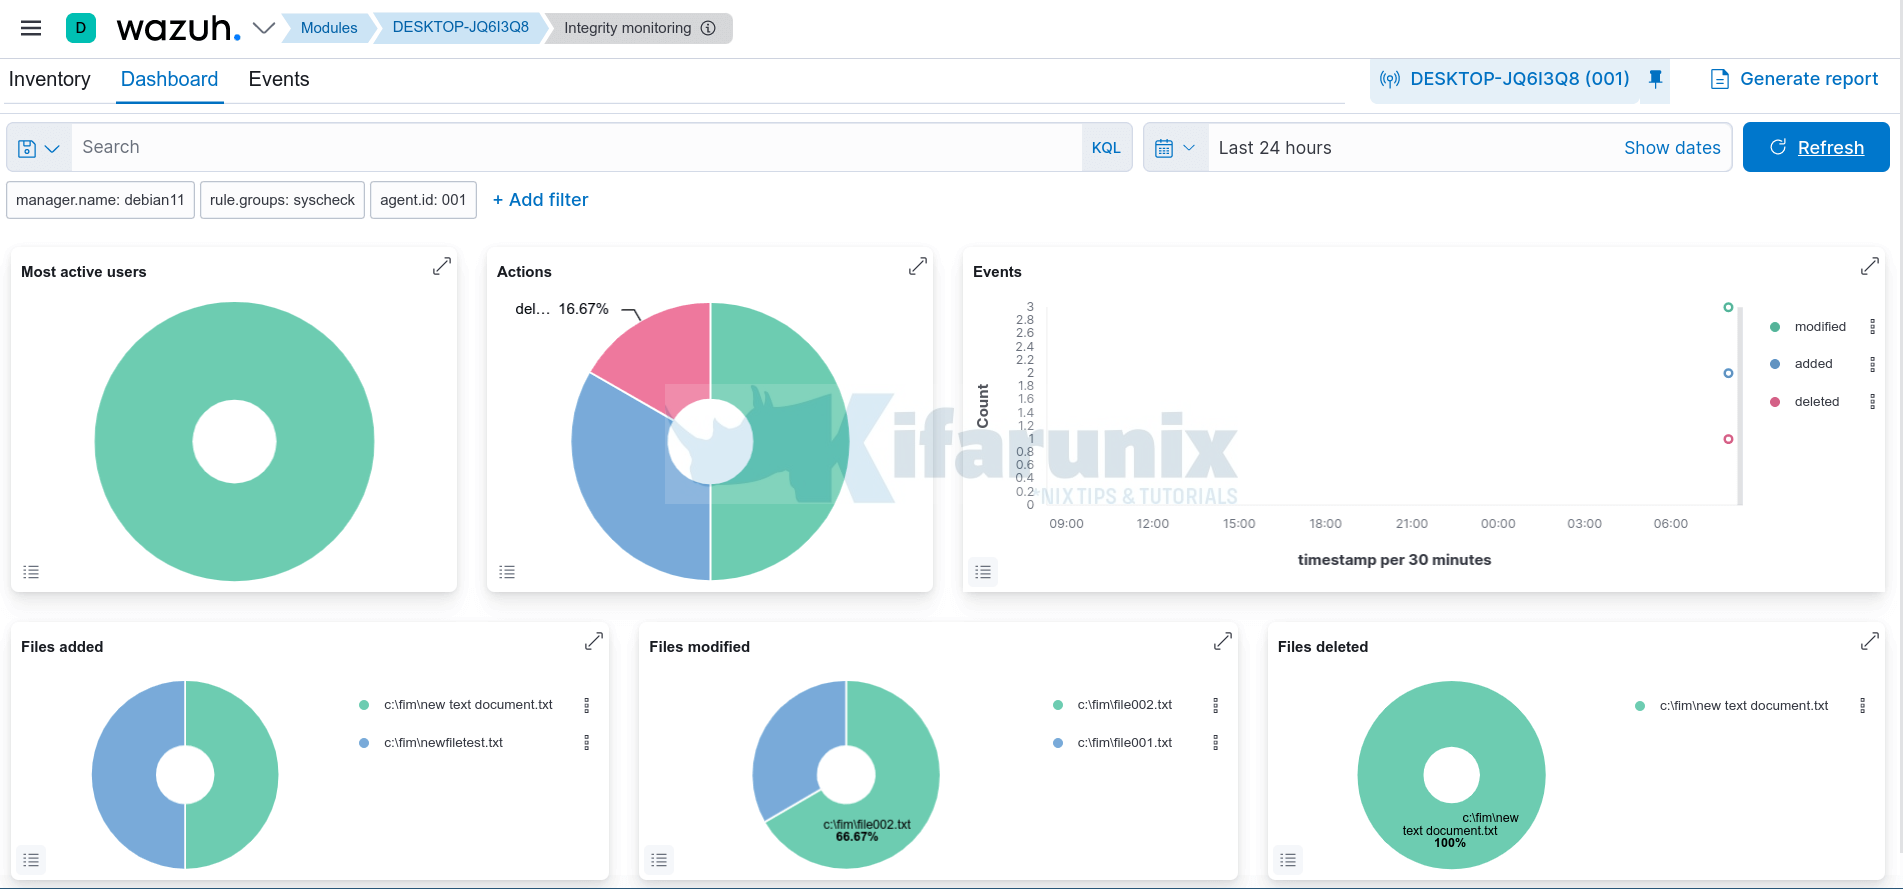
In this tutorial, you will learn how to monitor changes to critical files on Windows systems using Wazuh and ELK Stack. File operations are logged
This tutorial will show you how you can easily configure Logstash Elasticsearch Basic authentication. If you have secured your Elasticsearch cluster with authentication/authorization, then for
In this guide, we are going to learn how to install and setup TIG stack on Fedora 30 for monitoring system metrics such as memory,
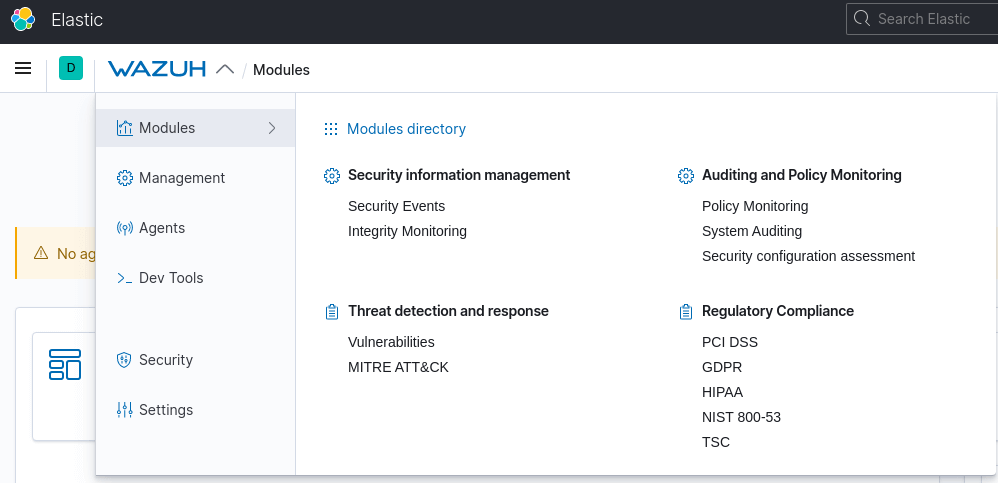
In this tutorial, you will learn how to integrate Wazuh manager with ELK stack as a unified Security Information and Event management tool. Wazuh consists
This guide presents a step-by-step tutorial on how to install OSSEC Agent on CentOS 8. OSSEC is an Open Source Host based Intrusion Detection System
In this tutorial, you will learn how to add or enroll Osquery hosts on Fleet manager. Fleet is the most widely used open source osquery