Update/Change Kibana Visualization Index Pattern
In this tutorial, you will learn how to update/change kibana visualization index pattern. Kibana is a free and open user interface that lets you visualize your
In this tutorial, you will learn how to update/change kibana visualization index pattern. Kibana is a free and open user interface that lets you visualize your
In this tutorial, you will learn how to easily configure Elasticsearch HTTPS Connection. You can configure your Beats; Filebeat, Metricbeat, Packetbeat, Logstash, Kibana, to securely
Follow through this tutorial to learn how to install Sensu Go on Debian 11. Sensu is an opensource infrastructure and application monitoring tool. Install Sensu
In this guide, we are going to learn how to install osquery on Debian 10 Buster. Osquery is an opensource tool that queries an operating
Follow through this tutorial to learn how create custom ELK ingest pipeline for custom log processing. Elastic Stack is so flexible that it can give
This tutorial will take you through how you can configure filebeat-elasticsearch authentication. You realize that when you enable Elastic basic authentication, you need to valid
In this blog post, we will cover how to configure centralized logging in OpenShift with LokiStack and ODF. If you manage an OpenShift cluster at
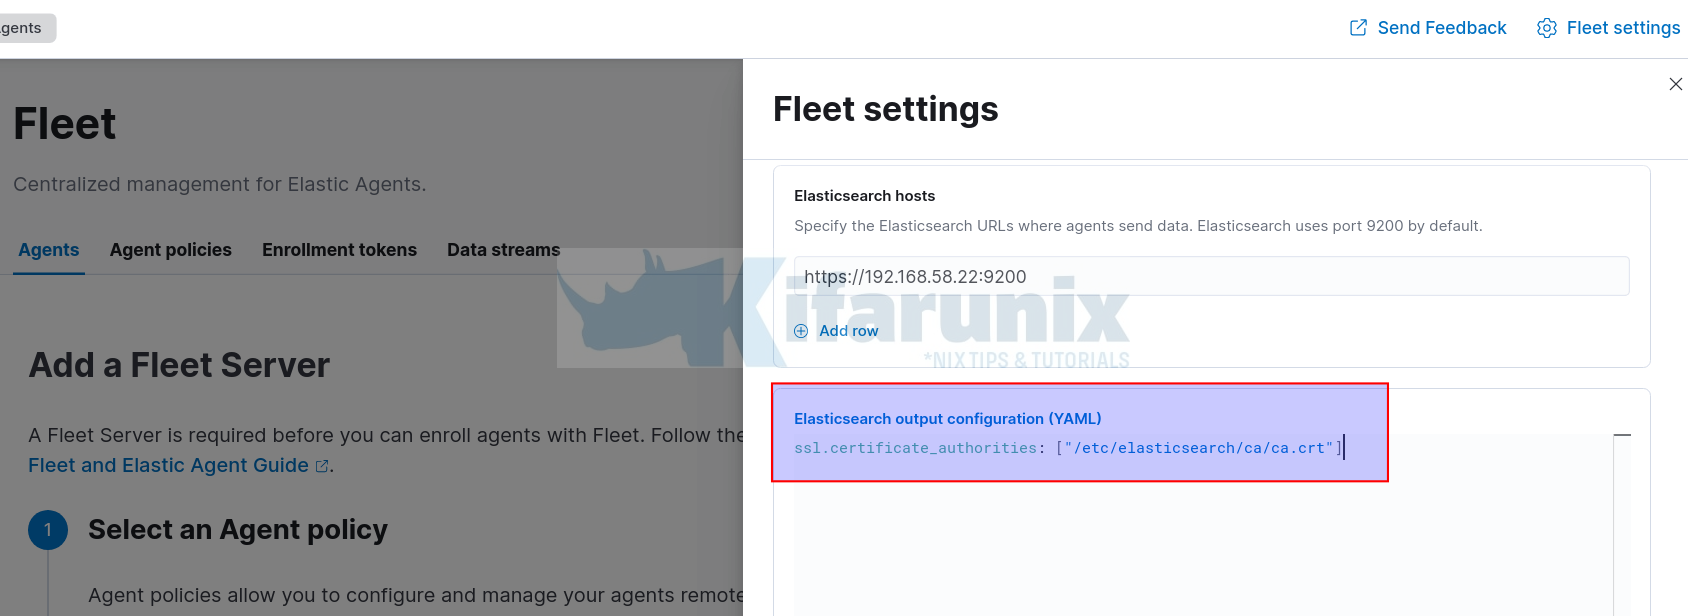
This tutorial will take you through how to ship system logs to ELK stack using Elastic Agents. You might be so used to using Elastic
In this guide, we are going to learn how to configure Nagios SNMP monitoring of Linux hosts. We will be using AlienVault USM/OSSIM as our
In this guide, we are going to learn how to configure NXLog to forward system logs to Rsyslog server on Ubuntu. There are various NXLog