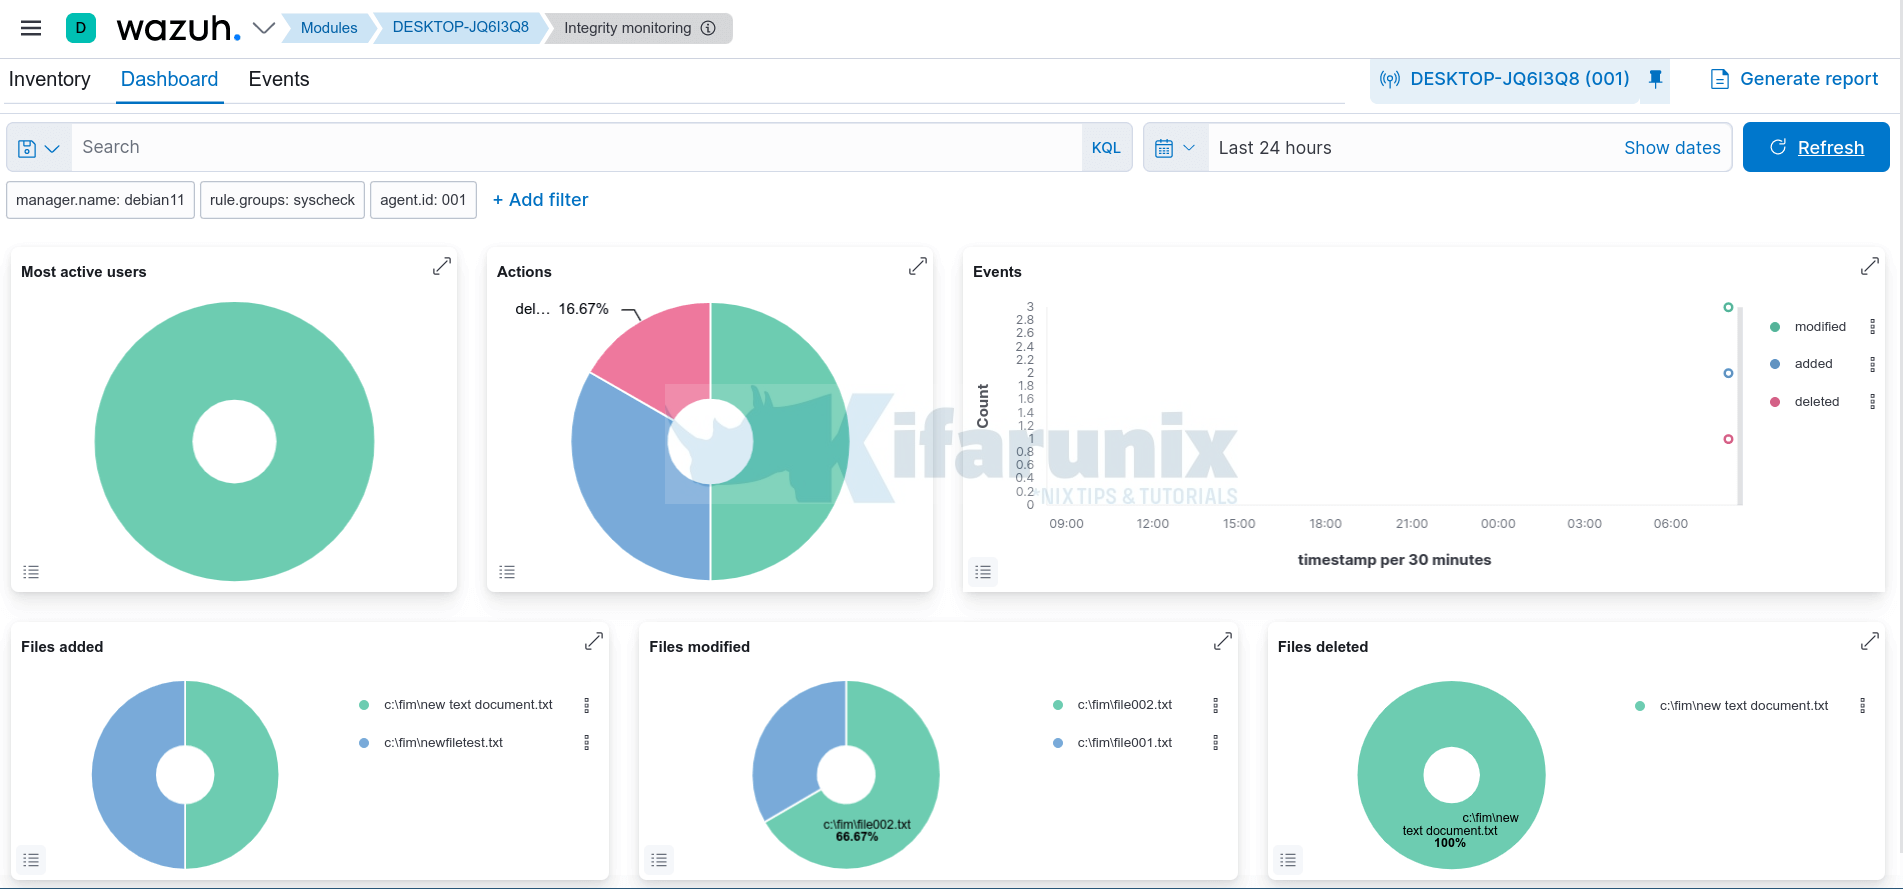
Monitor Changes to Critical Files on Windows Systems using Wazuh and ELK
In this tutorial, you will learn how to monitor changes to critical files on Windows systems using Wazuh and ELK Stack. File operations are logged
In this tutorial, you will learn how to monitor changes to critical files on Windows systems using Wazuh and ELK Stack. File operations are logged
Step through this guide to learn how to setup highly available Elasticsearch cluster with Keepalived. Setting up a highly available Elasticsearch cluster with Keepalived is
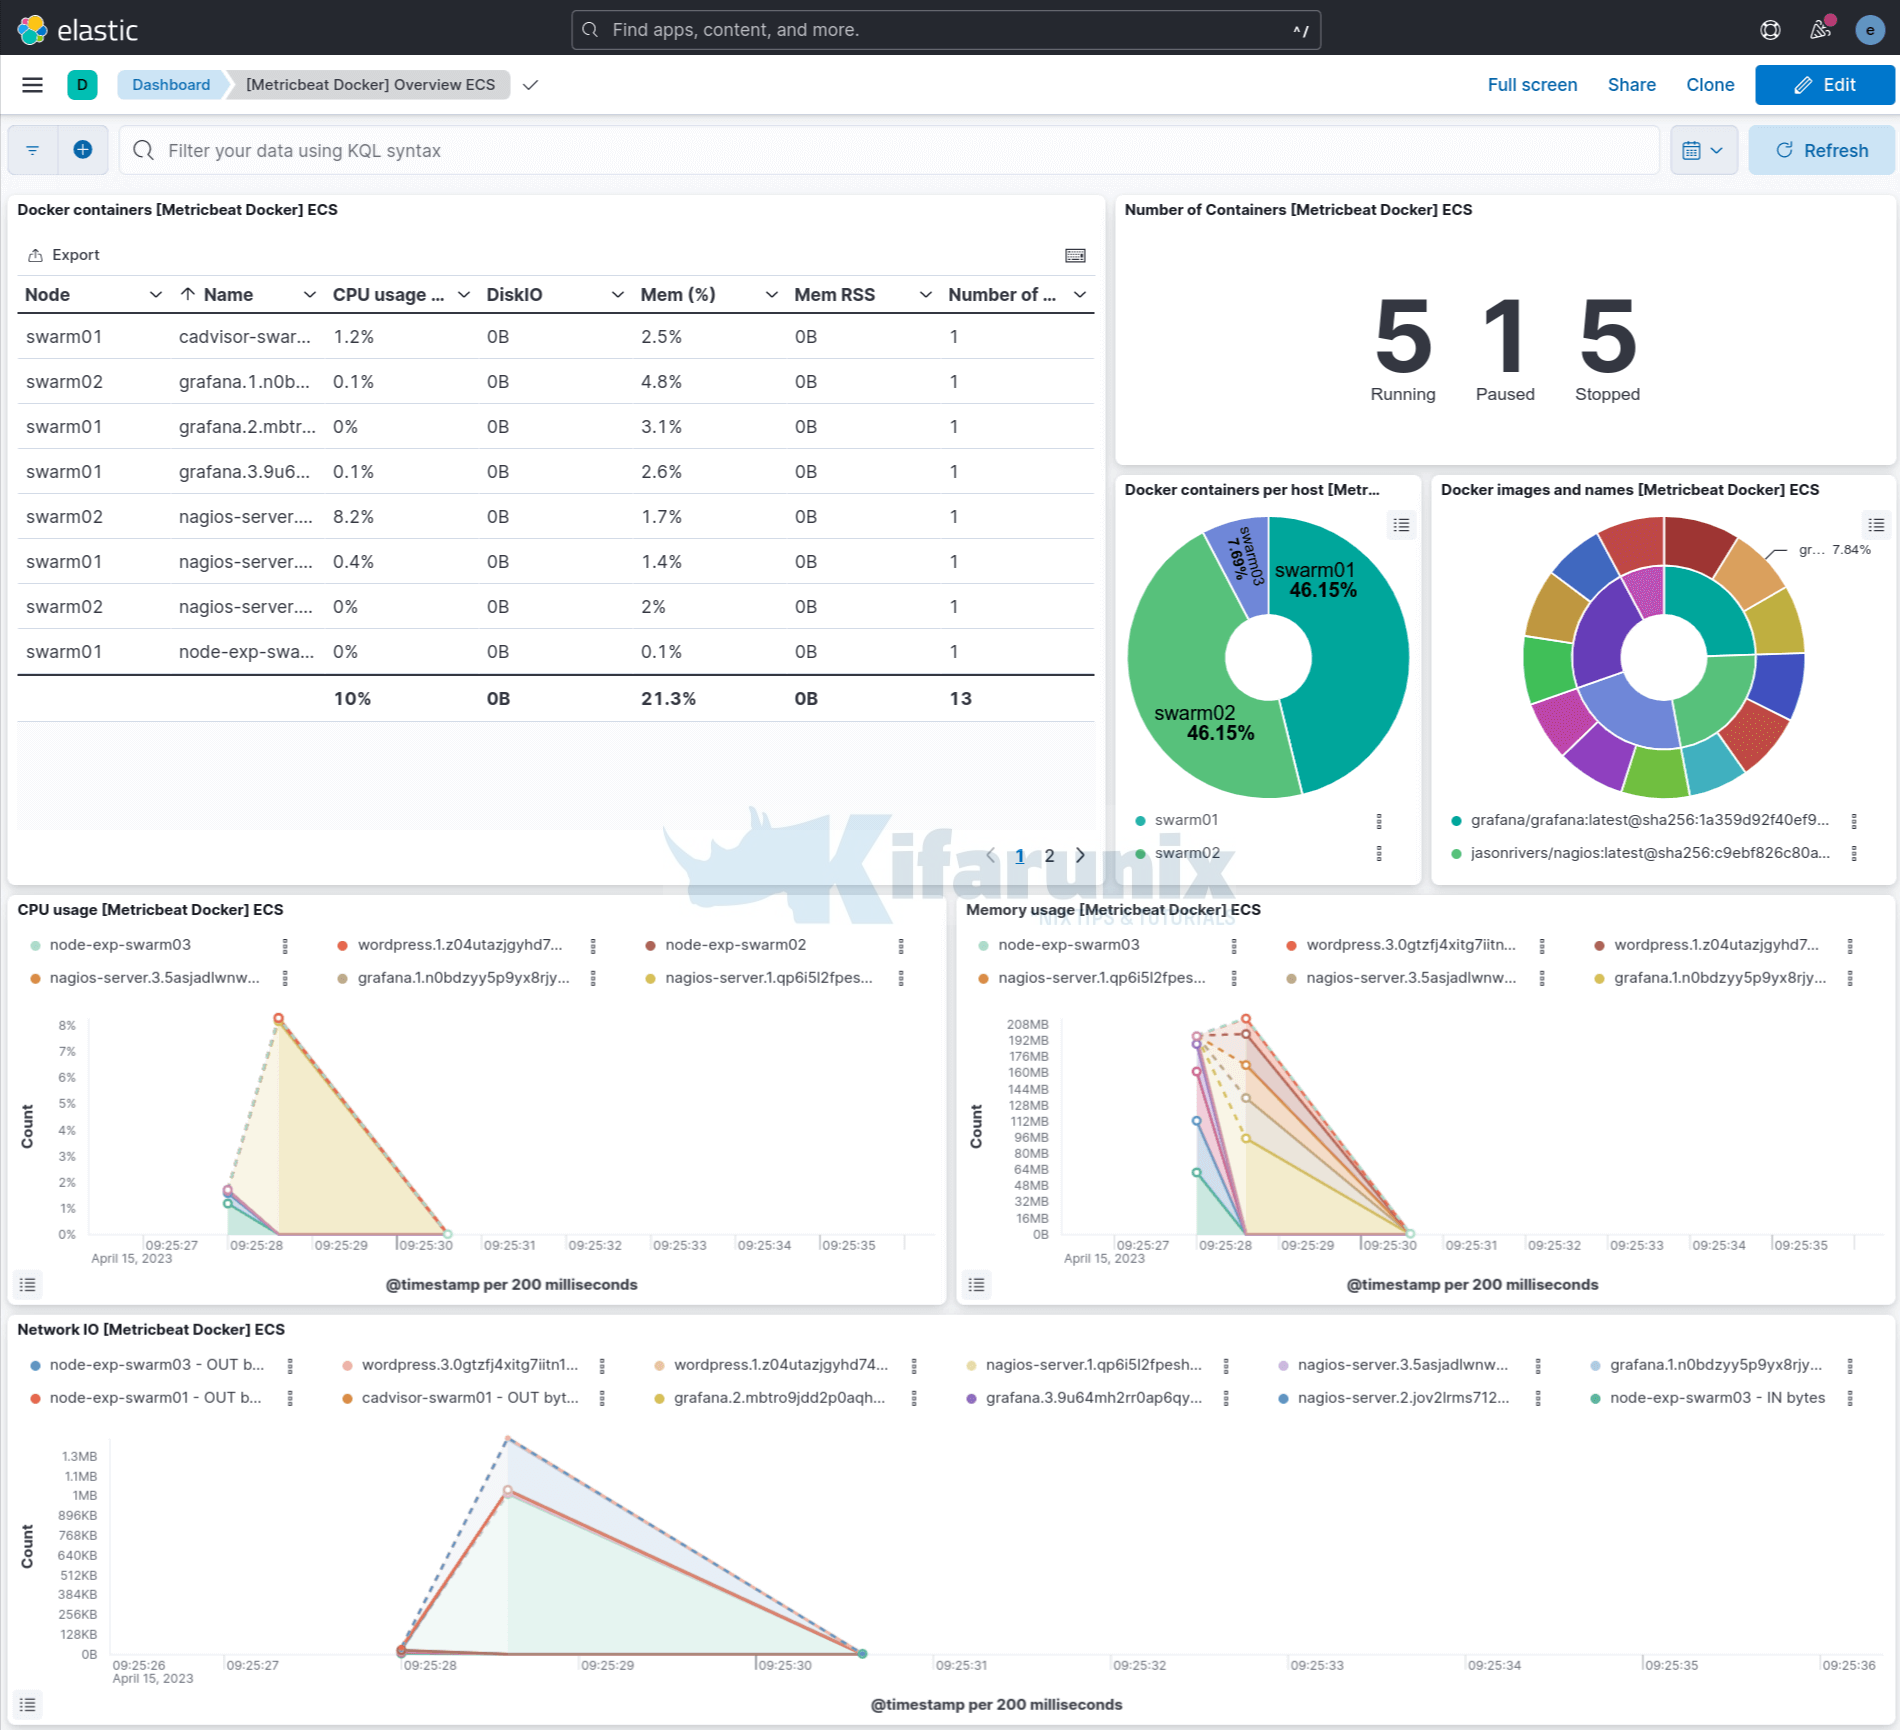
Is it possible to monitor Docker Swarm and container metrics using Metricbeat? Yes, of course! Metricbeat provides a flexible and powerful way to monitor Docker

In this tutorial, you will learn how to Monitor Disk Input/Output on Linux. In most cases whenever your Linux Server experience a performance slow down,
This guide will take you through how to configure Filebeat 8 to write logs to specific data stream. Are you collecting logs using Filebeat 8
This guide will focus on how to install Logstash 7 on Fedora 30/Fedora 29/CentOS 7 as a continuation of our guide on how to setup
In this tutorial, you will learn how to deploy ELK stack 8 Cluster on Docker using Ansible, an an open-source automation tool used for configuration
In this guide, we are going to go over how to create squid logs extractors on Graylog server. If you have pushed your Squid access
Hello there. In this tutorial, you will learn how to setup Kibana Elasticsearch and Fluentd on CentOS 8. Normally, you would setup Elasticsearch with Logstash,
Follow through this tutorial to learn how create custom ELK ingest pipeline for custom log processing. Elastic Stack is so flexible that it can give