Install ELK Stack on Ubuntu 20.04
Welcome to our guide on how to install ELK Stack on Ubuntu 20.04. ELK, currently known as Elastic Stack, is the acronym for open source
Welcome to our guide on how to install ELK Stack on Ubuntu 20.04. ELK, currently known as Elastic Stack, is the acronym for open source
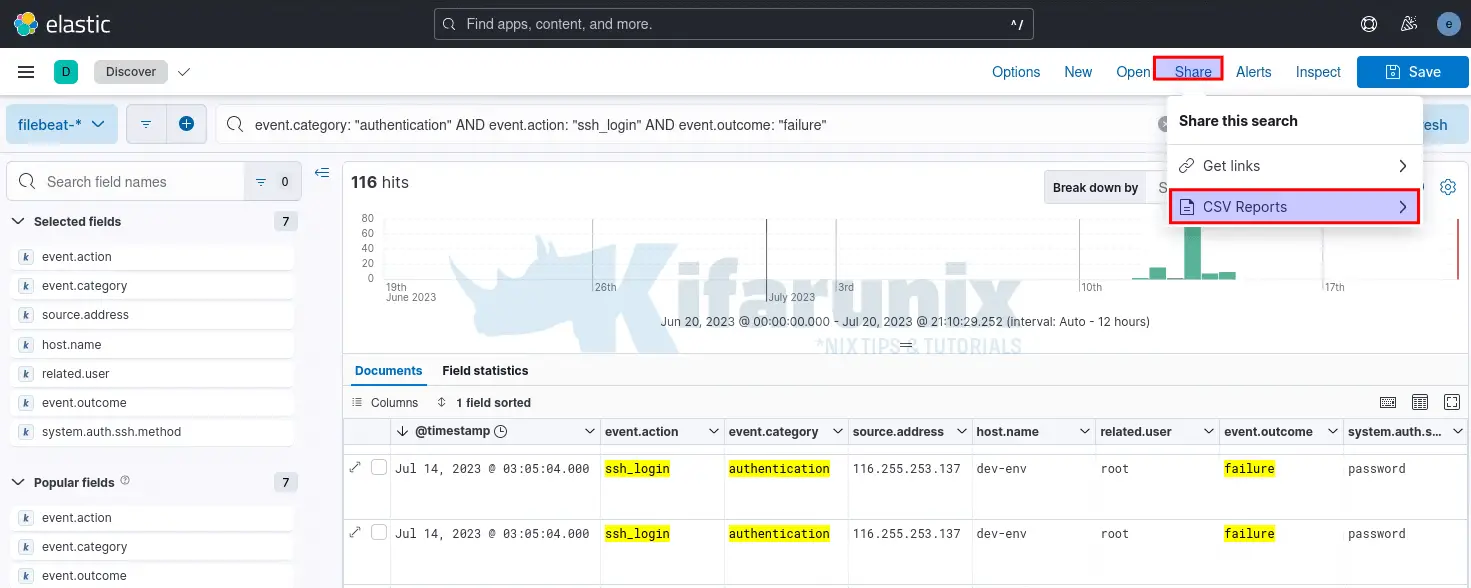
How can i easily export Kibana search results to CSV/Excel file? Well, that is an easy thing to do! Follow through this guide to learn
This tutorial will show you how you can easily configure Logstash Elasticsearch Basic authentication. If you have secured your Elasticsearch cluster with authentication/authorization, then for
This is a simple tutorial on how to search and delete specific records from Elasticsearch index. Elasticsearch ships with a delete_by_query API that enables you
In this tutorial, we will show you an easy way to configure Filebeat-Logstash SSL/TLS Connection. In order to sent encrypted data from Filebeat to Logstash,
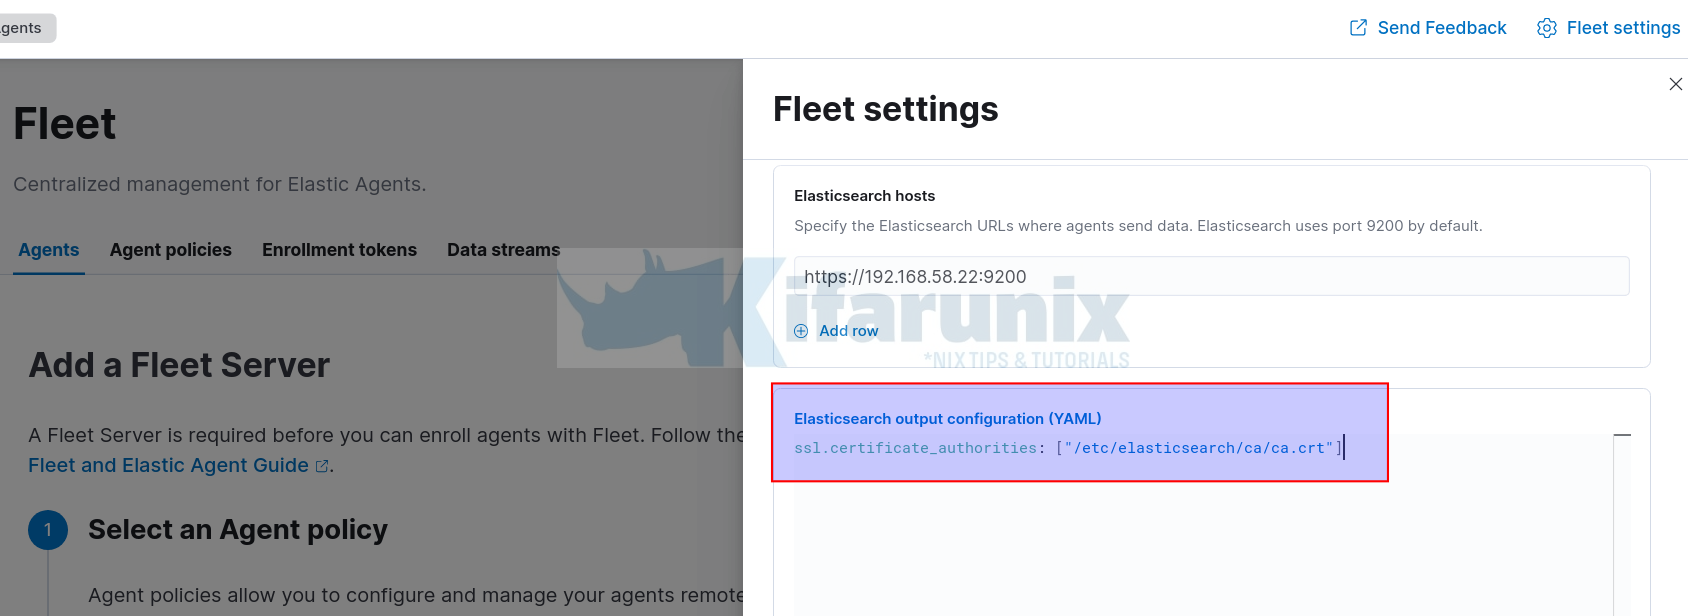
This tutorial will take you through how to ship system logs to ELK stack using Elastic Agents. You might be so used to using Elastic
Welcome to our guide on how to debug Logstash Grok filters. Grok filter uses regular expressions to parse unstructured event data into fields. It is
In this tutorial, you will learn how to enable basic authentication on ELK stack. Elastic/ELK stack supports user authentication. This enables it to restrict access
In this tutorial, we will try to show how to restore Elasticsearch snapshot to another Cluster. Elasticsearch data can be backed up by taking a
In this guide, we will walk you through easy steps to configure Kibana dashboards/visualizations to use custom index. Elastic Beats come packaged with sample Kibana