Update/Change Kibana Visualization Index Pattern
In this tutorial, you will learn how to update/change kibana visualization index pattern. Kibana is a free and open user interface that lets you visualize your
In this tutorial, you will learn how to update/change kibana visualization index pattern. Kibana is a free and open user interface that lets you visualize your
In this blog post, you will learn how to write specific events to specific index using Logstash. Logstash is a free and open server-side data
Follow through this tutorial to learn how to setup multinode Elasticsearch 9 cluster. As of this writing, Elastic Stack 9.0 is the current release. This
This guide will take you through how to configure Filebeat 8 to write logs to specific index. Are you collecting logs using Filebeat 8 and
This guide will focus on how to install and configure Logstash 7 on Ubuntu 18.04/Debian 9.8 as a continuation of our guide on how to
In this guide, we are going to learn how to install Elastic Stack 7 on Fedora 30/Fedora 29/CentOS 7. Elastic Stack comprises of: Elasticsearch is
This guide is about how to install Logstash 9 on Ubuntu/Debian as a continuation of our guide on how to setup Elastic Stack 9. We
In this tutorial, you will learn how to process and visualize ModSecurity Logs on ELK Stack. ModSecurity is an open source, cross-platform web application firewall
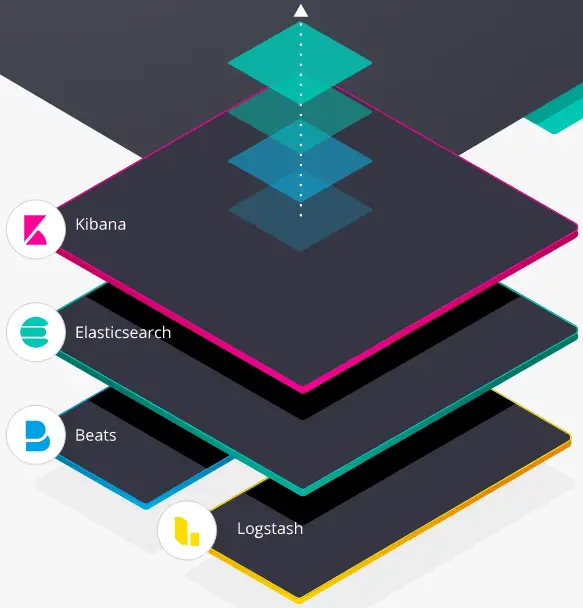
Today we are going to learn how to install Elasticsearch 7.x on Ubuntu 18.04/Debian 9.8. Elasticsearch is an open source, distributed, RESTful, JSON-based search and
How can I install Filebeat 8 on Debian 12? Well, the installation of Filebeat 8 on Debian 12 is no different from the rest of