Install Elasticsearch 7 on Fedora 30
In this guide, you are going to learn how to install Elasticsearch 7 on Fedora 30. We have covered similar installations in our previous guides. Install
In this guide, you are going to learn how to install Elasticsearch 7 on Fedora 30. We have covered similar installations in our previous guides. Install
Welcome to our tutorial on how to configure ELK Stack alerting with ElastAlert. As much as ELK Stack enables you to collect, process/parse, index and
This guide will focus on how to install and configure Logstash 7 on Ubuntu 18.04/Debian 9.8 as a continuation of our guide on how to
In this tutorial, you will learn how to run multiple filebeat instances in Linux system. Filebeat is one of the Elastic beat and is a
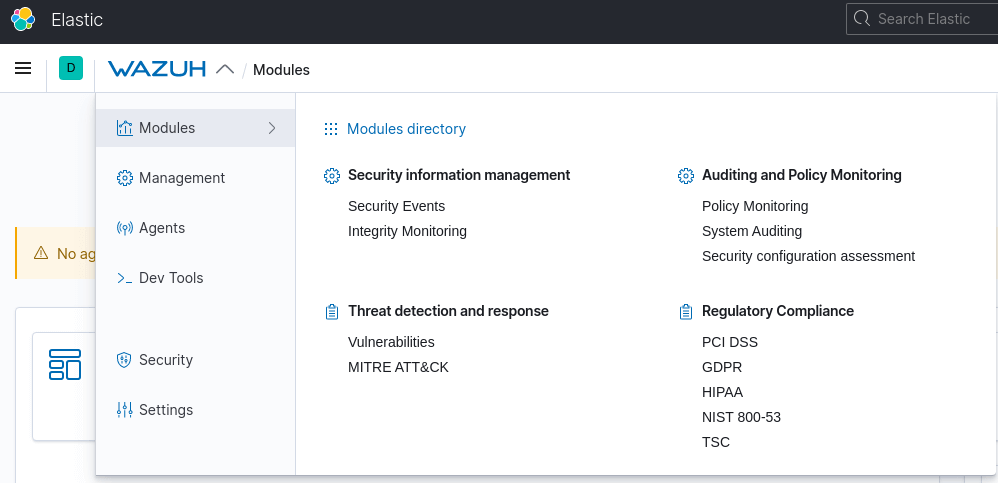
In this tutorial, you will learn how to integrate Wazuh manager with ELK stack as a unified Security Information and Event management tool. Wazuh consists
In this tutorial, you will learn how to install ELK stack 9.x on Ubuntu 24.04. Elastic/ELK stack 9.x has been released making it another major
Welcome to our guide on how to debug Logstash Grok filters. Grok filter uses regular expressions to parse unstructured event data into fields. It is
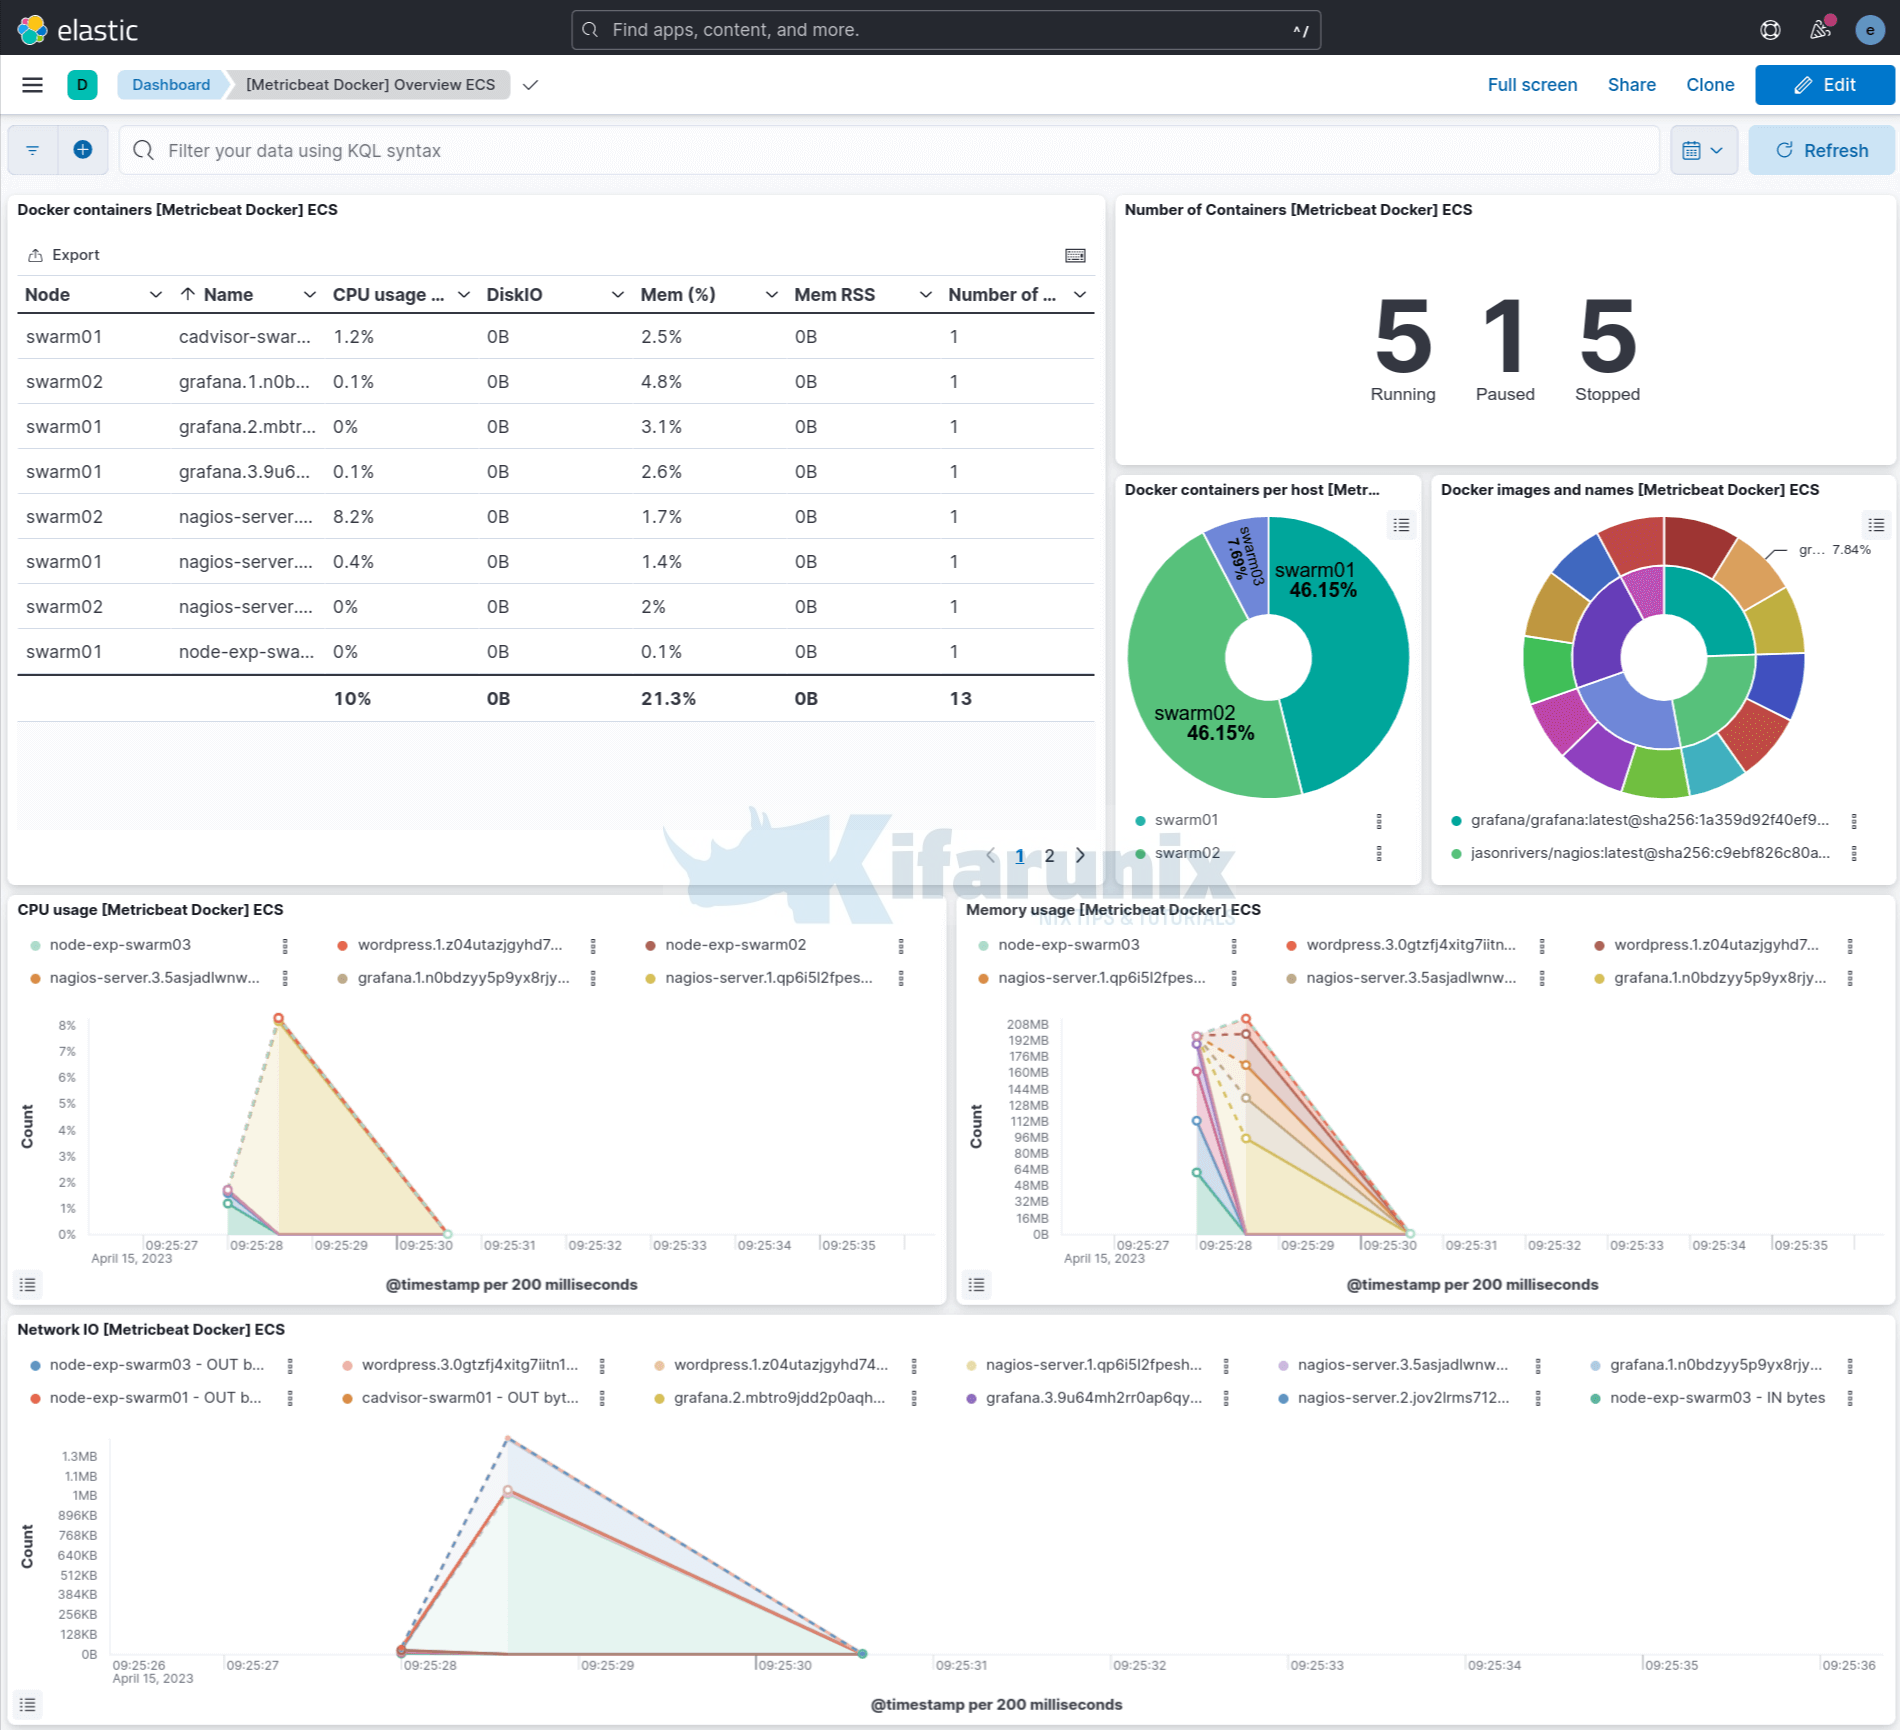
Is it possible to monitor Docker Swarm and container metrics using Metricbeat? Yes, of course! Metricbeat provides a flexible and powerful way to monitor Docker
In this tutorial, you will learn how to visualize WordPress user activity logs on ELK stack. WordPress do not provide an easy way to have
In this tutorial, you will learn how to install Wazuh agents on Ubuntu/Debian systems. Wazuh operates in server-client architecture. It is made up of a