How to Debug Logstash Grok Filters
Welcome to our guide on how to debug Logstash Grok filters. Grok filter uses regular expressions to parse unstructured event data into fields. It is
Welcome to our guide on how to debug Logstash Grok filters. Grok filter uses regular expressions to parse unstructured event data into fields. It is
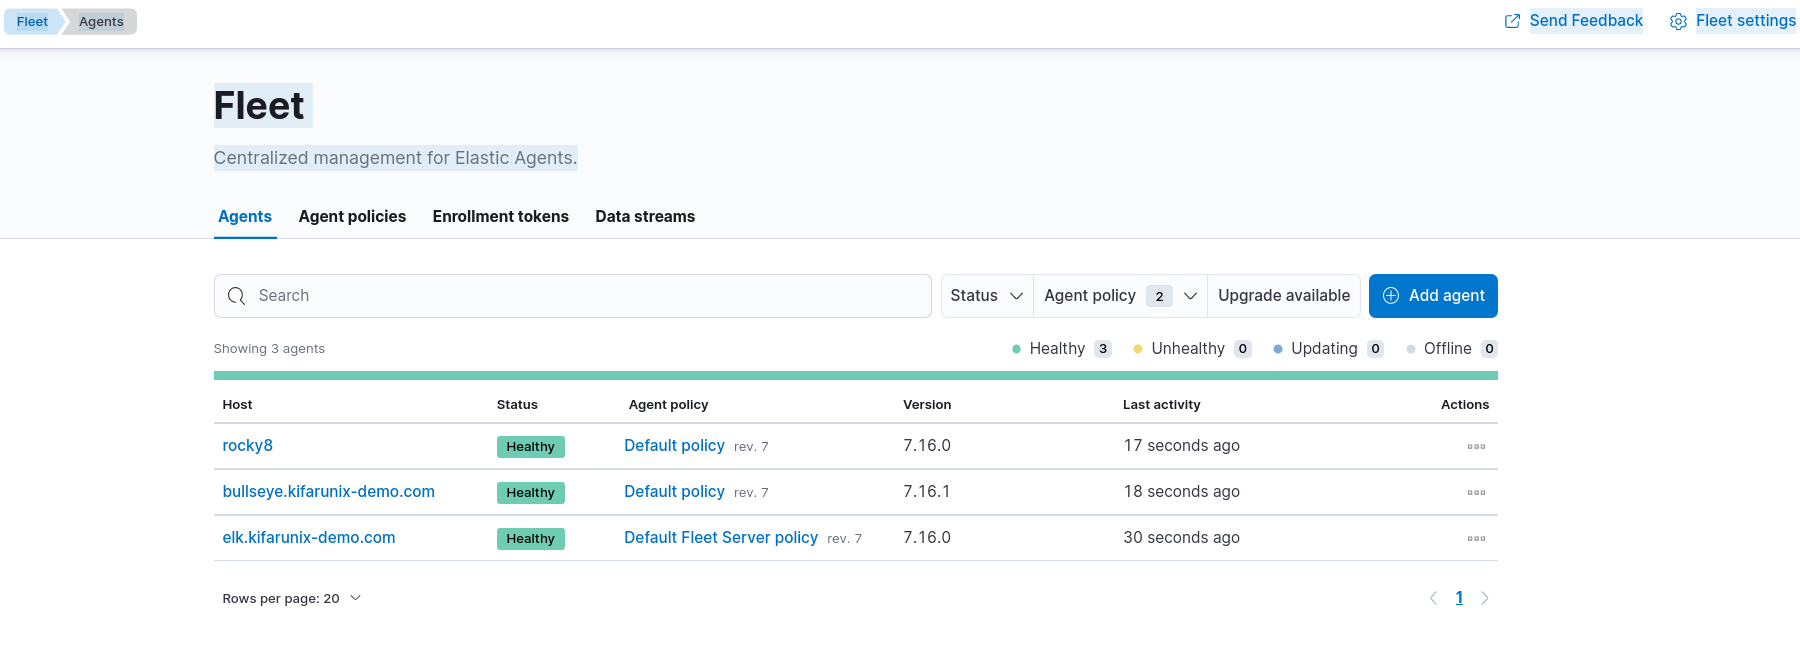
This tutorial will take you through how you can install and enroll Elastic agents to Fleet manager in Linux. According to Elastic Fleet and Elastic
How can I install Filebeat 8 on Debian 12? Well, the installation of Filebeat 8 on Debian 12 is no different from the rest of
In this guide, you will learn how to install Wazuh agent on pfSense. pfSense is the world’s most trusted opensource firewall which also doubles up
In this guide, we are going to learn how to setup multi-node Elasticsearch cluster. This guide has been tested on Fedora 30/Fedora 29/CentOS 7. So
This guide will take you through how to install Elasticsearch 7.x on CentOS 7/Fedora 29. Elasticsearch is the heart of Elastic Stack. Our previous guide
In this tutorial, you will learn how to update/change kibana visualization index pattern. Kibana is a free and open user interface that lets you visualize your
In this tutorial, you will learn how to easily configure Elasticsearch HTTPS Connection. You can configure your Beats; Filebeat, Metricbeat, Packetbeat, Logstash, Kibana, to securely
In this tutorial, you will learn how to process and visualize ModSecurity Logs on ELK Stack. ModSecurity is an open source, cross-platform web application firewall
Step through this guide to learn how to setup highly available Elasticsearch cluster with Keepalived. Setting up a highly available Elasticsearch cluster with Keepalived is