How to Debug Logstash Grok Filters
Welcome to our guide on how to debug Logstash Grok filters. Grok filter uses regular expressions to parse unstructured event data into fields. It is
Welcome to our guide on how to debug Logstash Grok filters. Grok filter uses regular expressions to parse unstructured event data into fields. It is
Follow through this guide to learn how to install Filebeat on FreeBSD. Installing Filebeat on FreeBSD Filebeat is not available on the default FreeBSD repositories
Hello there. Today we are going to learn how to install Graylog 3.0 on CentOS 7. Graylog is a leading open-source log management tool that
This tutorial will show you how you can easily configure Logstash Elasticsearch Basic authentication. If you have secured your Elasticsearch cluster with authentication/authorization, then for
In this tutorial, you will learn how to enable HTTPS connection between Elasticsearch nodes. One of the Elastic security features is to enable encryption between
Welcome to our guide on how to install and configure SNMP on CentOS 8. SNMP stands for Simple Network Management Protocol. It is an Internet Standard protocol that provides
This guide will take you through how to configure Filebeat 8 to write logs to specific data stream. Are you collecting logs using Filebeat 8
In this guide, we are going to learn how to add hosts to Nagios Server for monitoring. Well, in order to monitor your remote hosts
How to upgrade Elasticsearch 7 to 8? In this guide, you will learn how to upgrade ELK Stack 7.x to ELK Stack 8.x. ELK/Elastic 8
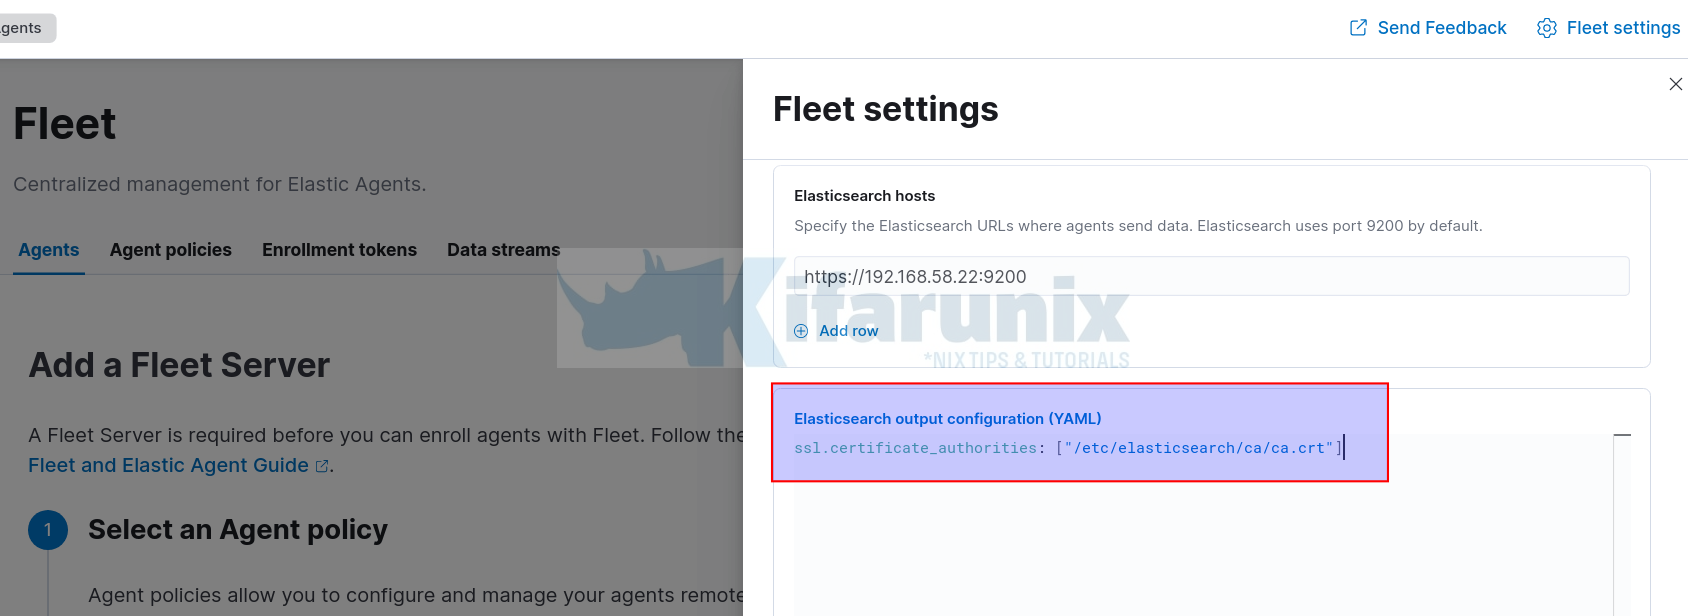
This tutorial will take you through how to ship system logs to ELK stack using Elastic Agents. You might be so used to using Elastic