Create Custom ELK Ingest Pipeline for Custom Log Processing
Follow through this tutorial to learn how create custom ELK ingest pipeline for custom log processing. Elastic Stack is so flexible that it can give
Follow through this tutorial to learn how create custom ELK ingest pipeline for custom log processing. Elastic Stack is so flexible that it can give
In this guide, we are going to learn how to install OSSEC agent on Mac OS X. Installing OSSEC Agent on Mac OS X Well
This guide describes how to easily install Nagios NRPE agents on Debian 11/Debian 10. If you want to monitor your Debian hosts using Nagios server,
In this very tutorial, you are going learn how to monitor hosts and services with Icinga 2 on Ubuntu 18.04 LTS. Well, Icinga 2 can
This guide is about how to configure SNMP version 3 on Debian 9. There are three major versions of SNMP that have so far been

In this tutorial, you will learn how to Monitor Disk Input/Output on Linux. In most cases whenever your Linux Server experience a performance slow down,
How can I configure Filebeat to send logs to Kafka? This is a complete guide on configuring Filebeat to send logs to Kafka. Filebeat is
Follow through this guide to learn how to install latest Graylog on CentOS 7. Graylog is a leading open-source log management tool that provides real time collection,
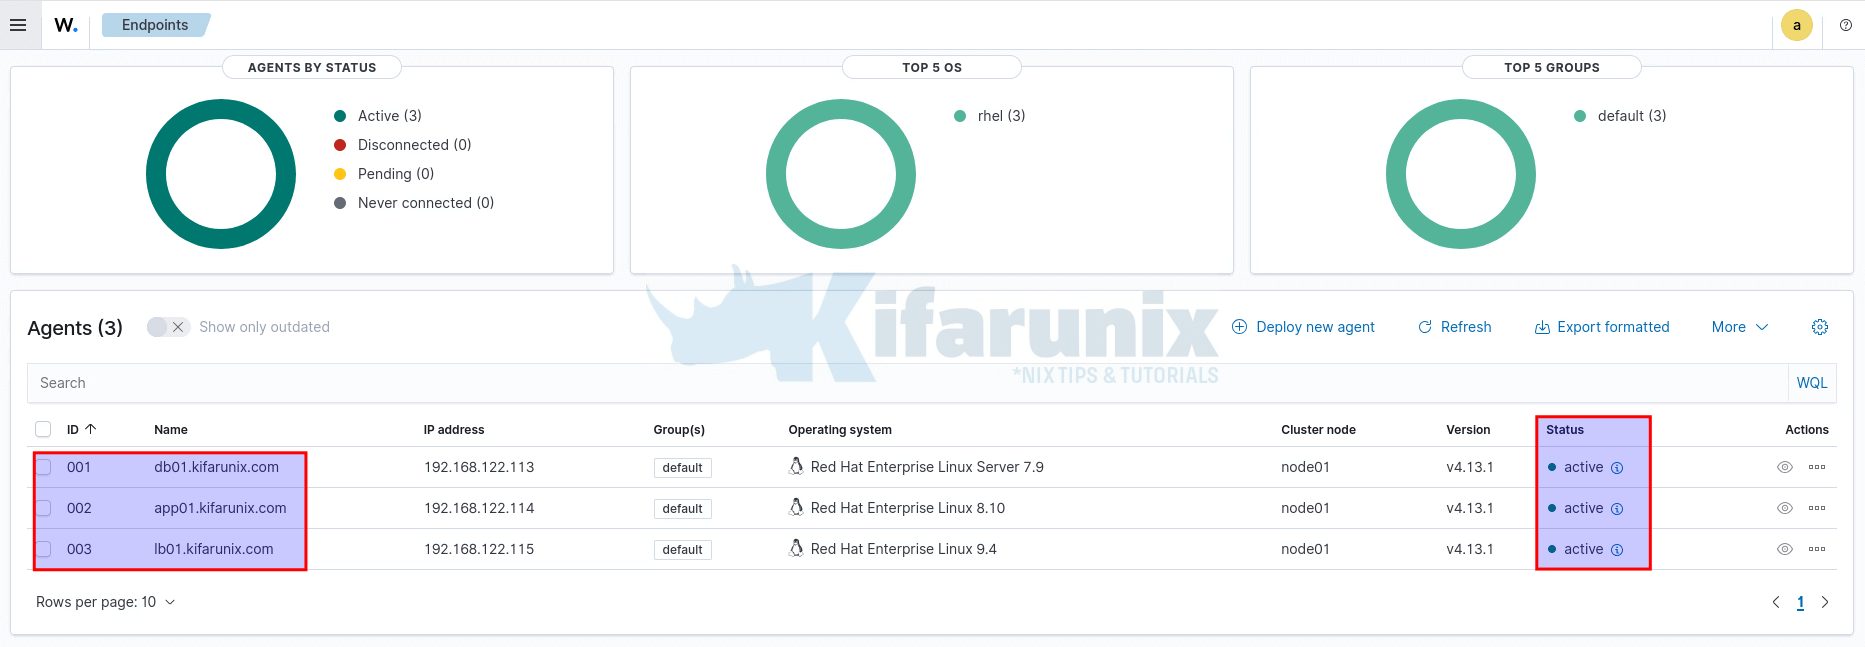
In this tutorial, you will learn how to install Wazuh agent on RHEL 8/9/10. Our previous setup was on setting up Wazuh server with ELK
In this tutorial, you will learn how to process and visualize ModSecurity Logs on ELK Stack. ModSecurity is an open source, cross-platform web application firewall