Monitor Squid Access Logs with Graylog Server
Welcome to our tutorial on how to monitor squid access logs with Graylog server. Graylog is a leading open-source log management tool that provides real time
Welcome to our tutorial on how to monitor squid access logs with Graylog server. Graylog is a leading open-source log management tool that provides real time
Follow through this tutorial to learn how to setup multinode Elasticsearch 8.x cluster. As of this writing, Elastic Stack 8.3 is the current release. This
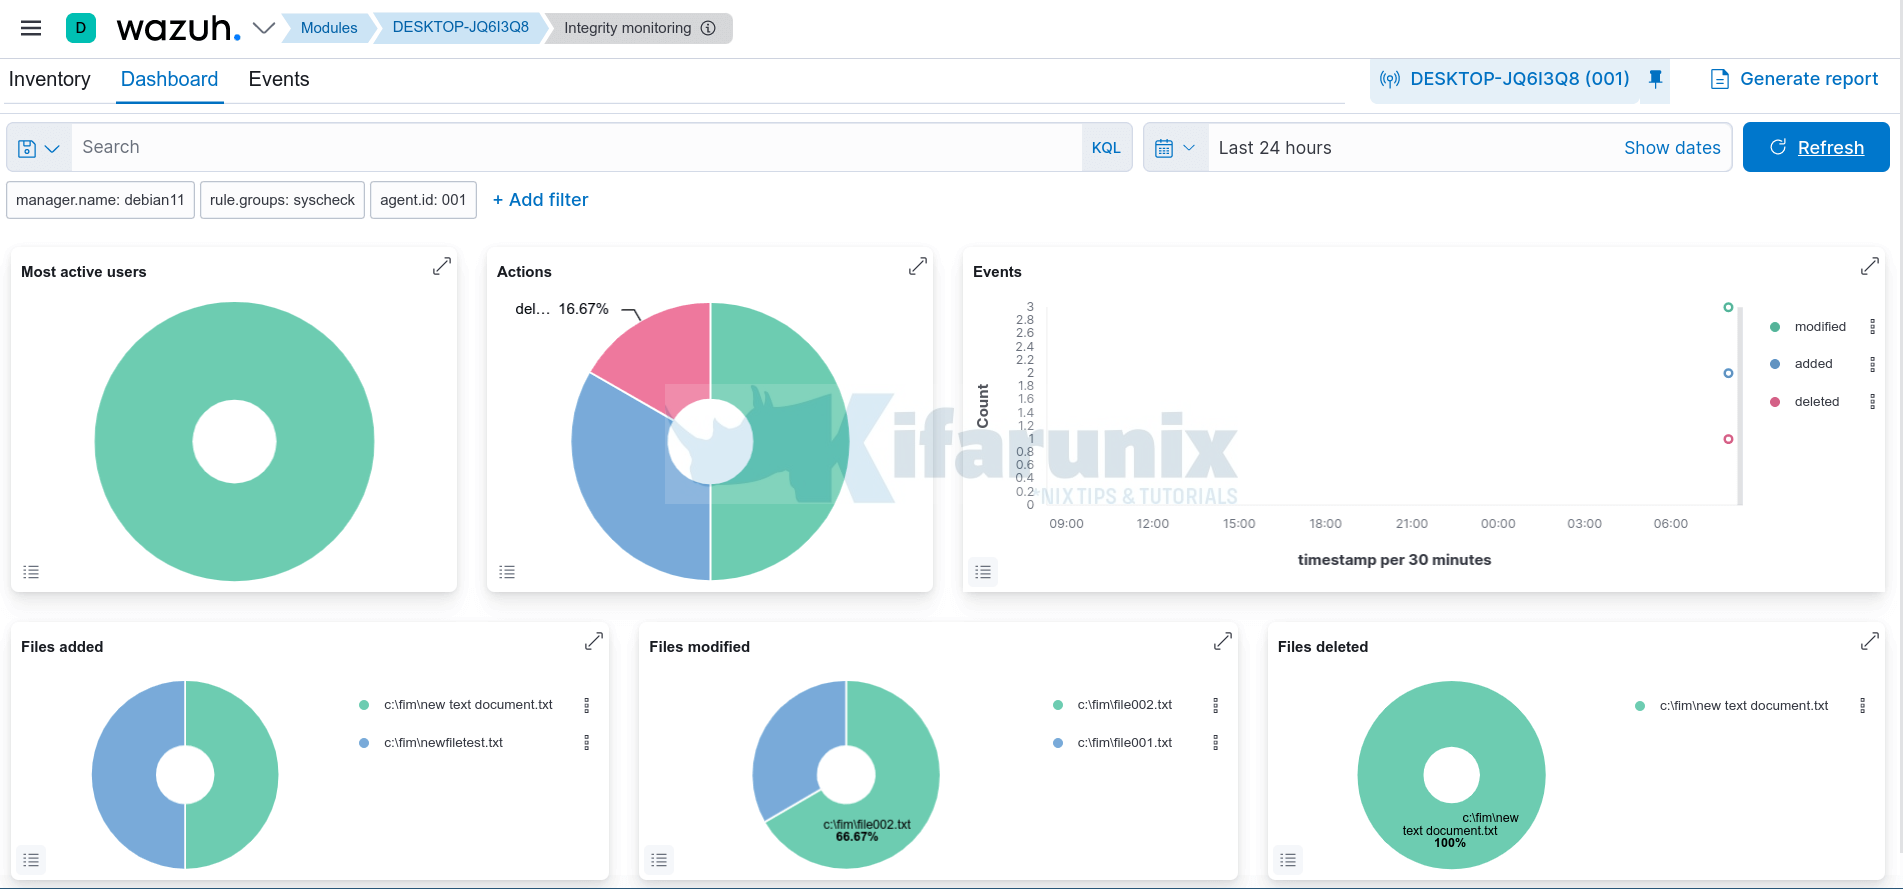
In this tutorial, you will learn how to monitor changes to critical files on Windows systems using Wazuh and ELK Stack. File operations are logged
Follow through this guide to learn how to install latest Graylog on CentOS 7. Graylog is a leading open-source log management tool that provides real time collection,
Well, assuming you understand the implications of the expired SSL/TLS certificates, let us go through how to monitor SSL/TLS Certificates Expiry with Nagios. Nagios provides
In this guide, we are going to learn how to install Nagios on Debian 11. Nagios is an opensource tool that provides an enterprise-class central monitoring engine
This guide will take you through how to install Sensu agent on Ubuntu/Debian systems. We are using Ubuntu 22.04 and Debian 11 specifically on this
In this guide, we are going to learn how to install OSSEC Agent on Debian 10 Buster. OSSEC is an open source host intrusion detection
This guide will take you through how to install Elasticsearch 7.x on CentOS 7/Fedora 29. Elasticsearch is the heart of Elastic Stack. Our previous guide
In this tutorial, we will try to show how to restore Elasticsearch snapshot to another Cluster. Elasticsearch data can be backed up by taking a