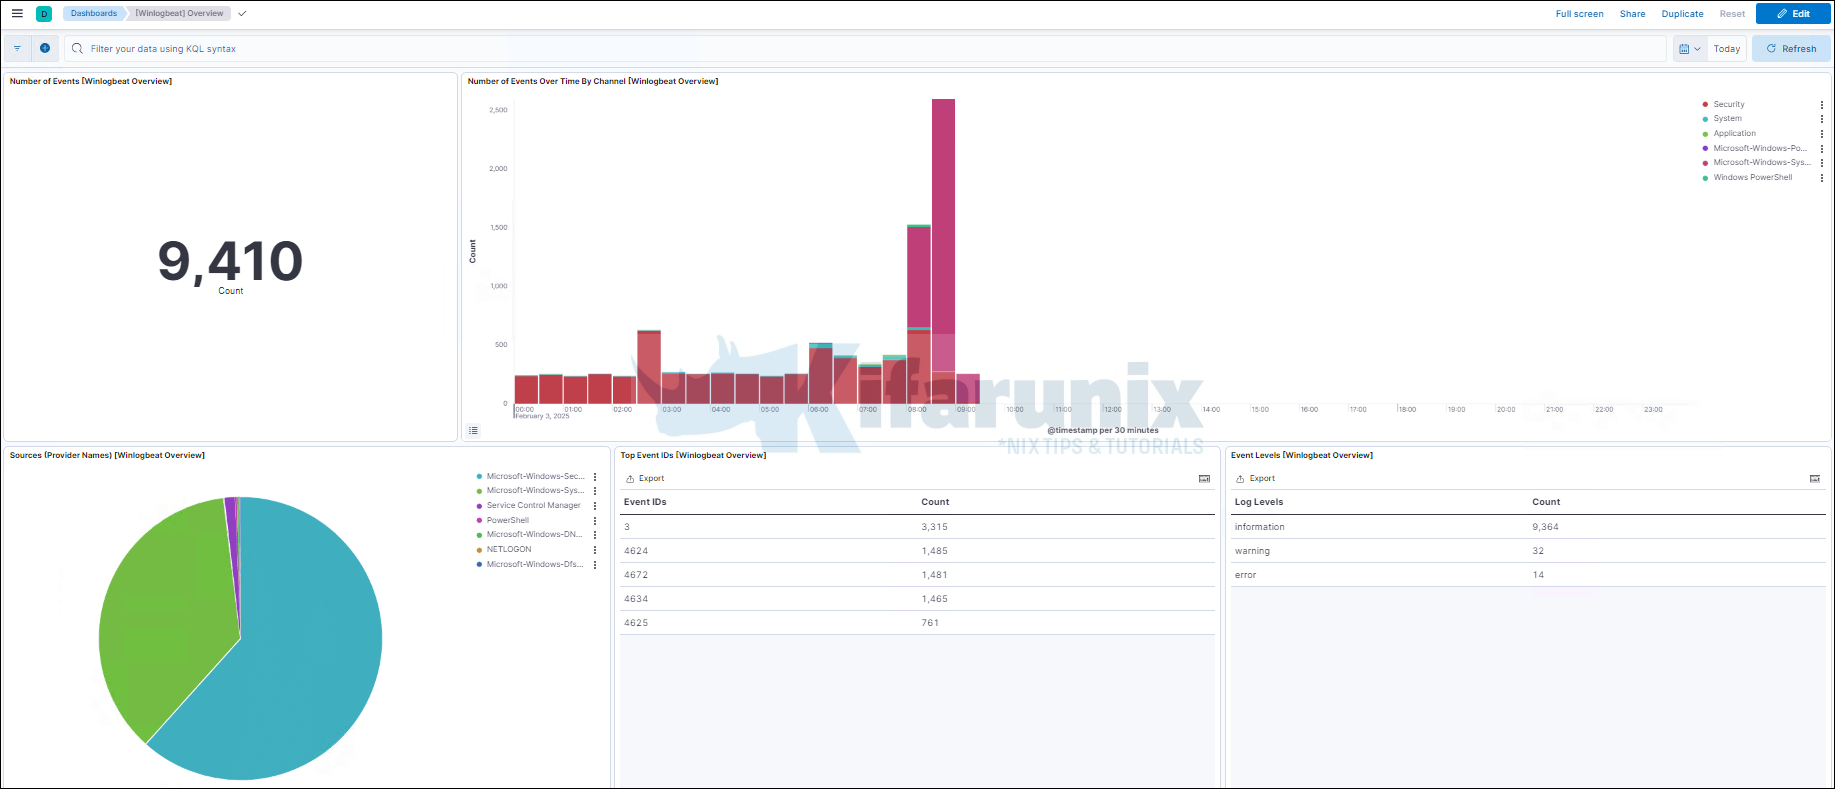
Send Windows logs to Elastic Stack using Winlogbeat and Sysmon
In this guide, we are going to learn how to send Windows logs to Elastic Stack using Winlogbeat and Sysmon. Winlogbeat is an Elastic Beat
In this guide, we are going to learn how to send Windows logs to Elastic Stack using Winlogbeat and Sysmon. Winlogbeat is an Elastic Beat
In this tutorial, we will try to show how to restore Elasticsearch snapshot to another Cluster. Elasticsearch data can be backed up by taking a
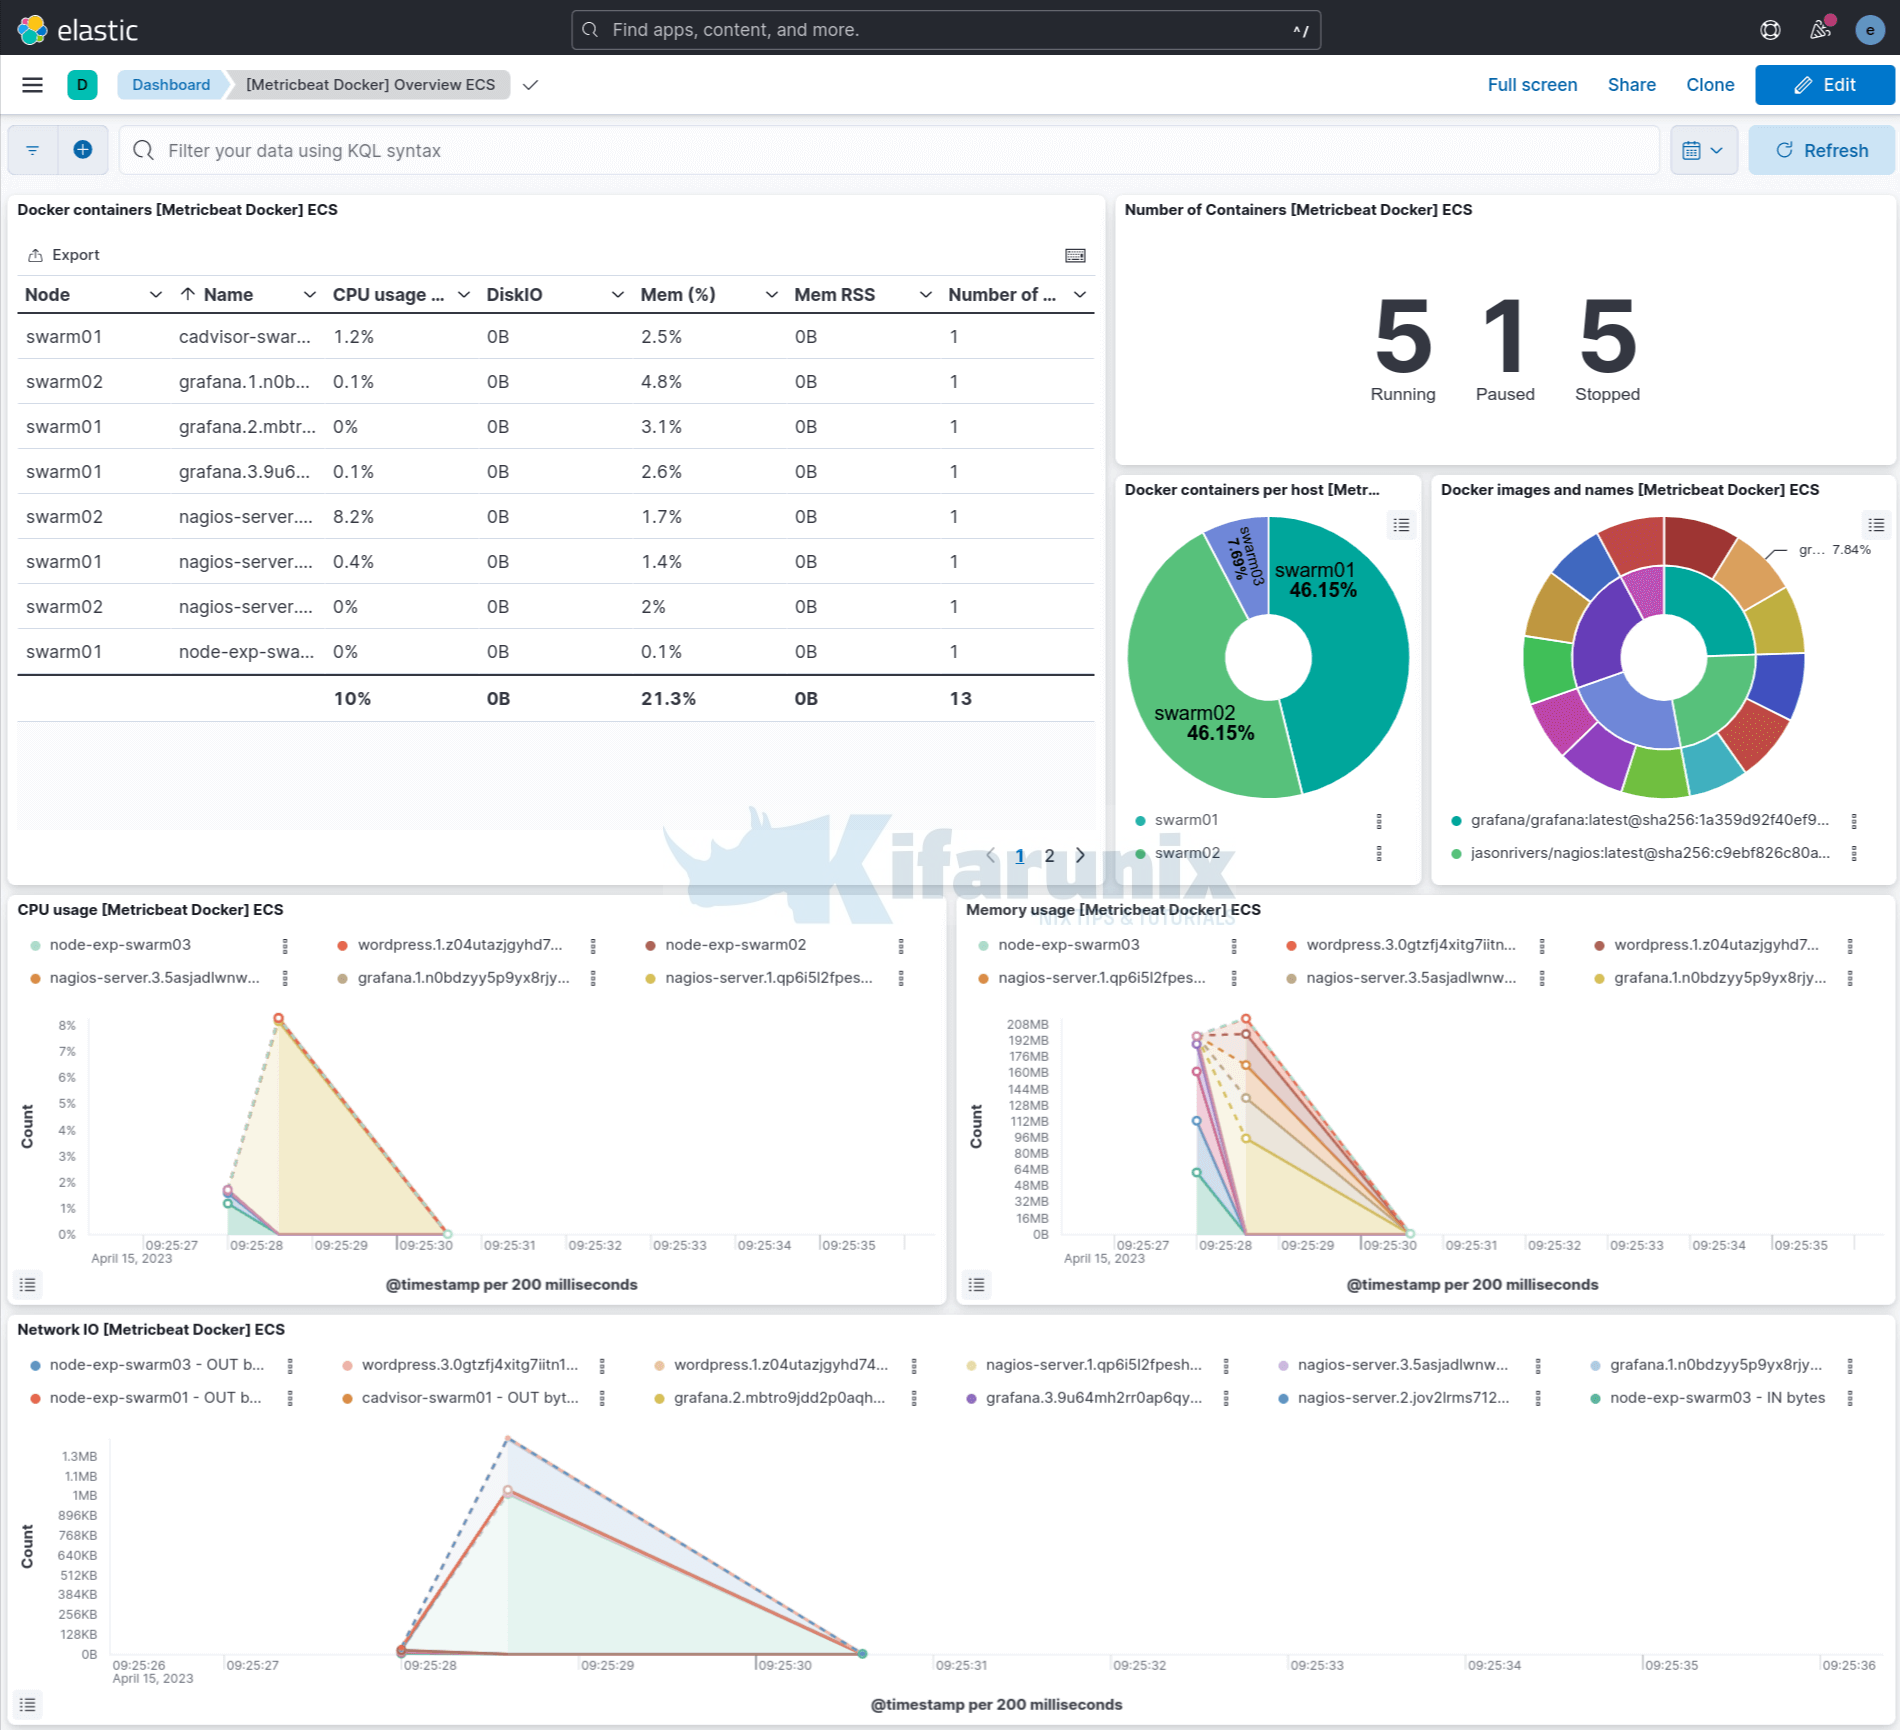
Is it possible to monitor Docker Swarm and container metrics using Metricbeat? Yes, of course! Metricbeat provides a flexible and powerful way to monitor Docker
In this tutorial, you will learn how to easily configure Elasticsearch HTTPS Connection. You can configure your Beats; Filebeat, Metricbeat, Packetbeat, Logstash, Kibana, to securely
In this tutorial, we are going to learn how to install and configure Filebeat on CentOS 8. Filebeat is one of the Elastic Stack beats,
In this tutorial, you will learn how to install Wazuh agents on Ubuntu/Debian systems. Wazuh operates in server-client architecture. It is made up of a
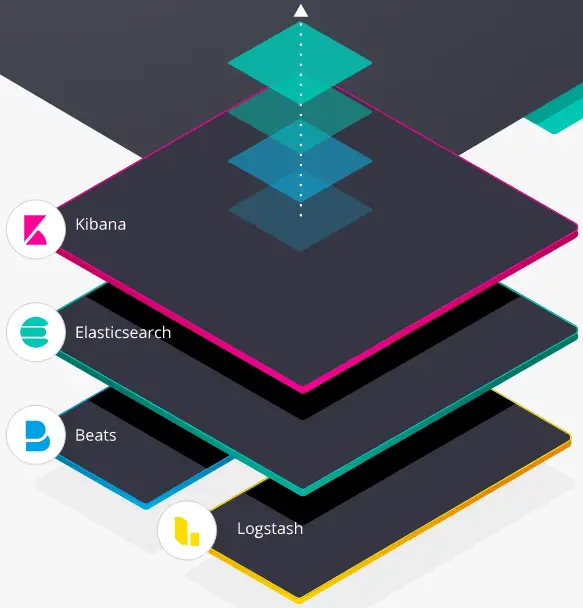
This tutorial will guide on how to install Elastic Stack 7 on Ubuntu 18.04/Debian 9.8. We will be discussing the installation and configuration of each
How do I change the log retention policy in elk stack? In this tutorial, you will learn how to configure log retention period in ELK
In this guide, you will learn how to install Wazuh agent on pfSense. pfSense is the world’s most trusted opensource firewall which also doubles up
This tutorial will show you how you can easily configure Logstash Elasticsearch Basic authentication. If you have secured your Elasticsearch cluster with authentication/authorization, then for